Build / Security
WordPress malware removal and security hardening.
Hacked site, spam pages, unknown admin users or fake orders? We clean WordPress and WooCommerce properly, close the way in and harden the site so it stays clean.
What’s included
A full clean-up, not just a scan: we remove the infection and the reason it happened.
Malware and backdoor removal
Infected files, injected code, spam posts and hidden backdoors cleaned from files and the database.
Unauthorised user removal
Rogue administrator accounts removed and all passwords and keys rotated.
Updates and patching
WordPress core, themes and plugins updated; abandoned or nulled plugins replaced.
Security hardening
File editing disabled, XML-RPC and user enumeration closed, security headers and login protection added.
WooCommerce fraud protection
Rate limiting and custom rules to stop card-testing and bot orders.
Blacklist and search clean-up
Spam URLs removed from Google and warnings cleared where the site was flagged.
Who it’s for
Website owners dealing with a hacked WordPress site, spam content, redirects to strange sites, or a WooCommerce store flooded with fraudulent orders.
Platforms and tools
- WordPress
- WooCommerce
- PHP
- Server logs
- Google Search Console
- Custom security plugins
How we work
Contain
Back up the current state and stop the damage.
Investigate
Find how attackers got in: vulnerable plugins, weak logins or leftover backdoors.
Clean
Remove malware, spam content and rogue users from files and database.
Harden
Update everything and close the weaknesses that were used.
Protect
Add monitoring and, for stores, fraud controls that fit the actual attack.
Related work
Security work on real client websites.
Questions, answered.
Can’t find what you’re looking for? Ask us directly.
How quickly can you start?
We usually start as soon as we have access. Tell us the site address and what you are seeing, and we will reply with next steps.
Will my website be offline?
Normally not. Most clean-ups happen with the site online. If a site is actively harming visitors we may recommend a short maintenance mode.
Can you stop fake WooCommerce orders?
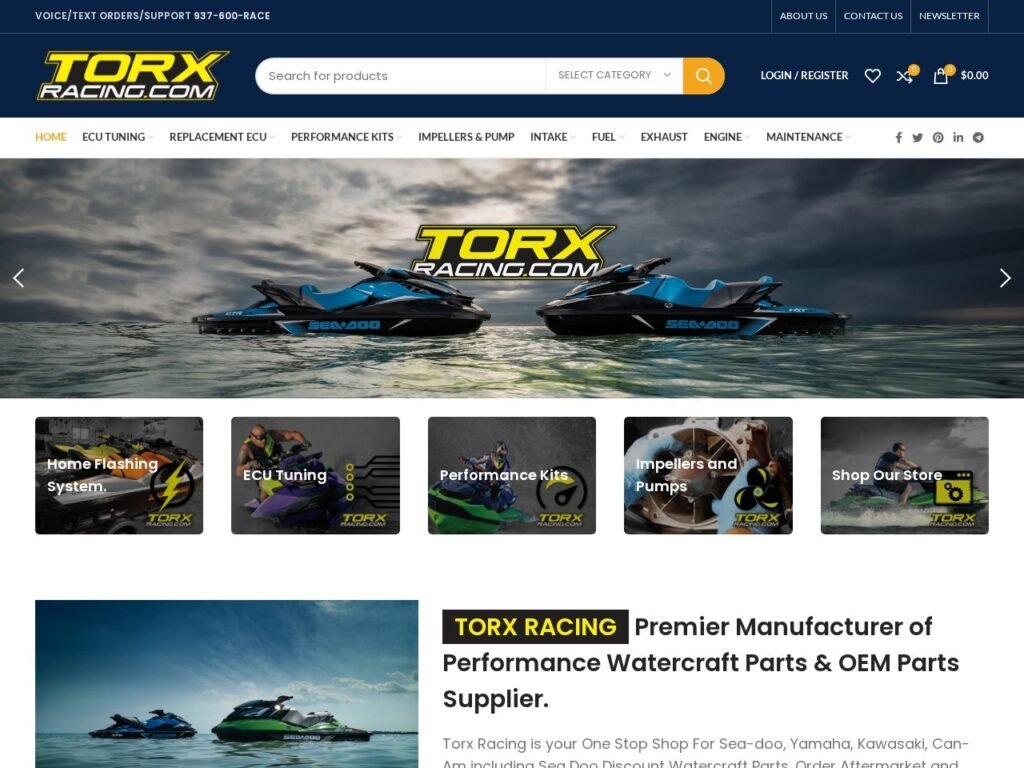
Yes. For TORX Racing we built a custom plugin with checkout rate limiting, IP blocking and a lockdown mode that stopped card-testing orders while real orders continued.
How do I stop it happening again?
Keep everything updated, remove unused plugins, use strong unique passwords and two-factor login, and keep backups. We can set this up for you.
Guides from our blog
Has your WordPress site been hacked?
Tell us what is happening. We’ll clean it up, secure it and explain what went wrong.